The patch installed successfully. So why is the vulnerability still in the scan report?
The patch installed successfully. So why is the vulnerability still in the scan report?
Before calling it a false positive, check what actually changed.
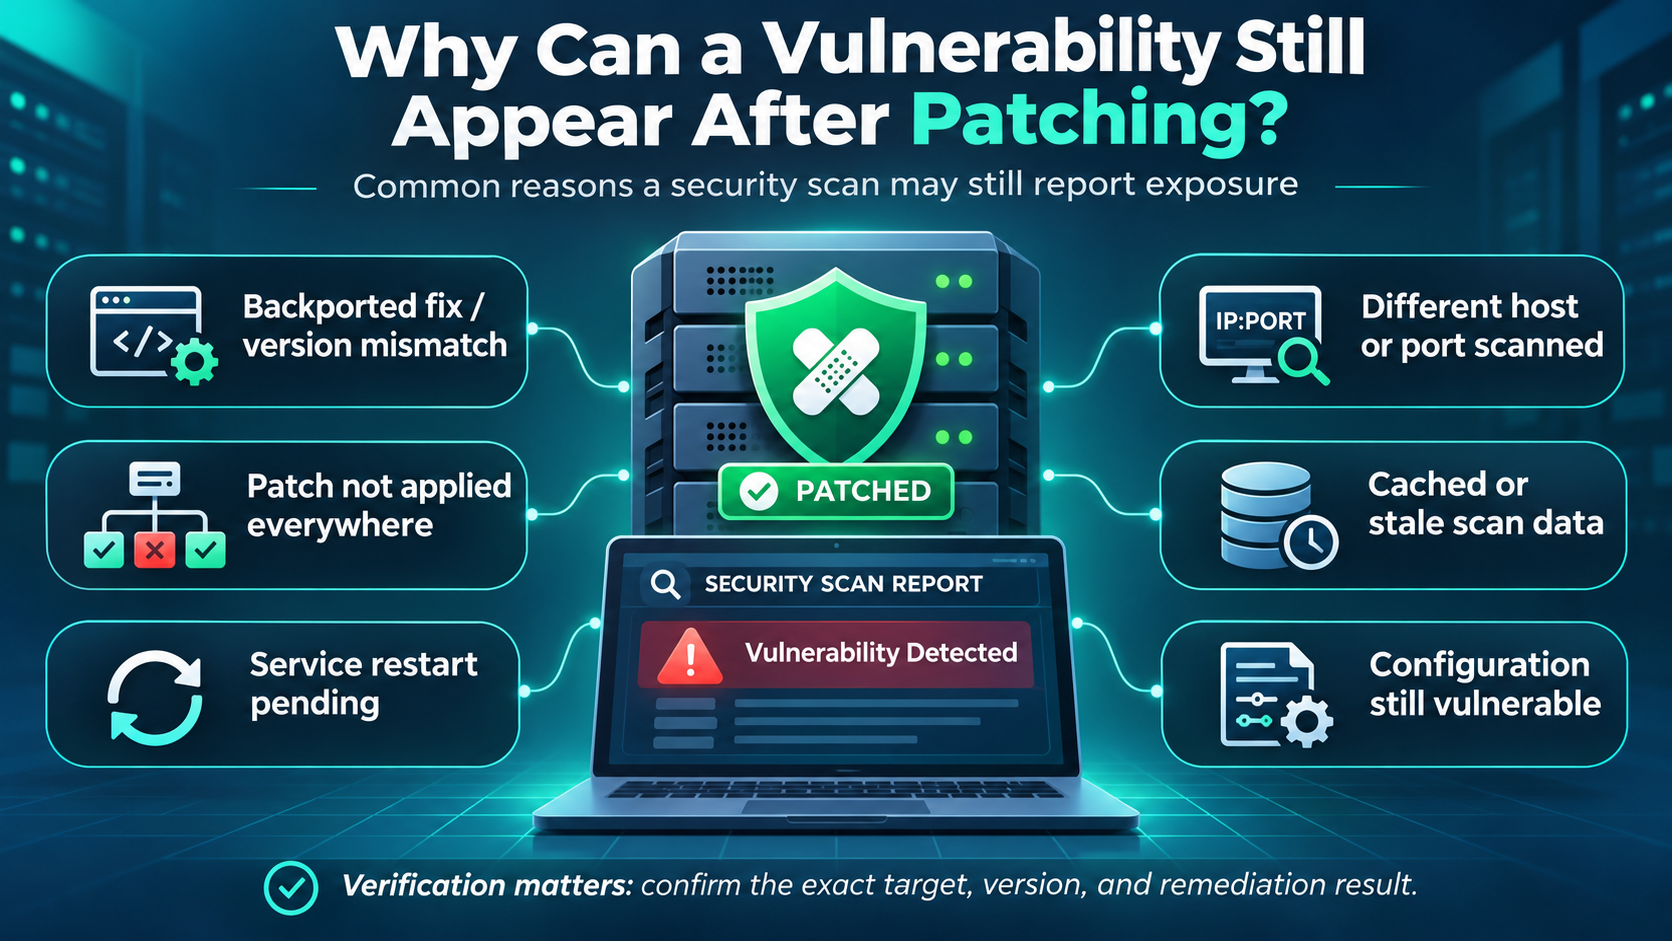
The service may still be running older code. One application instance may have missed the update. Or a version-based check may not recognize a backported security fix.
Also check the basics: the exact host and port, when the evidence was collected, and whether the finding requires a configuration change rather than another update.
The opposite mistake matters too: a blocked or incomplete scan is not proof of a fix.
Our new SecPoint guide explains six possible causes and a practical verification workflow.
Read the guide:
https://www.secpoint.com/vulnerability-still-detected-after-patching.html
Get a FREE vulnerability scan:
https://www.secpoint.com/free-vulnerability-scan.html
Become a SecPoint partner:
https://www.secpoint.com/partner-signup.html
#VulnerabilityScanning #PatchManagement #CyberSecurity #Penetrator #SecPoint