How to Achieve True High Availability on Dedicated Servers with BGP IP Failover
How to Achieve True High Availability on Dedicated Servers with BGP IP Failover 🌐
If you manage infrastructure, you know that keeping your services online during a server crash is critical. For years, VRRP (using tools like Keepalived) has been the go-to solution for High Availability (HA). But VRRP has a major limitation: it requires your servers to share the same local Layer 2 network.
When you move to isolated dedicated servers or across different racks, Layer 2 is often not an option. This is where BGP (Border Gateway Protocol) becomes the gold standard.
Unlike VRRP, BGP IP failover allows you to announce a public IP from two entirely separate machines. If your primary server fails, the datacenter's router seamlessly forwards traffic to the backup. Nobody moves an IP by hand. Nobody opens a panic support ticket at 3 AM.
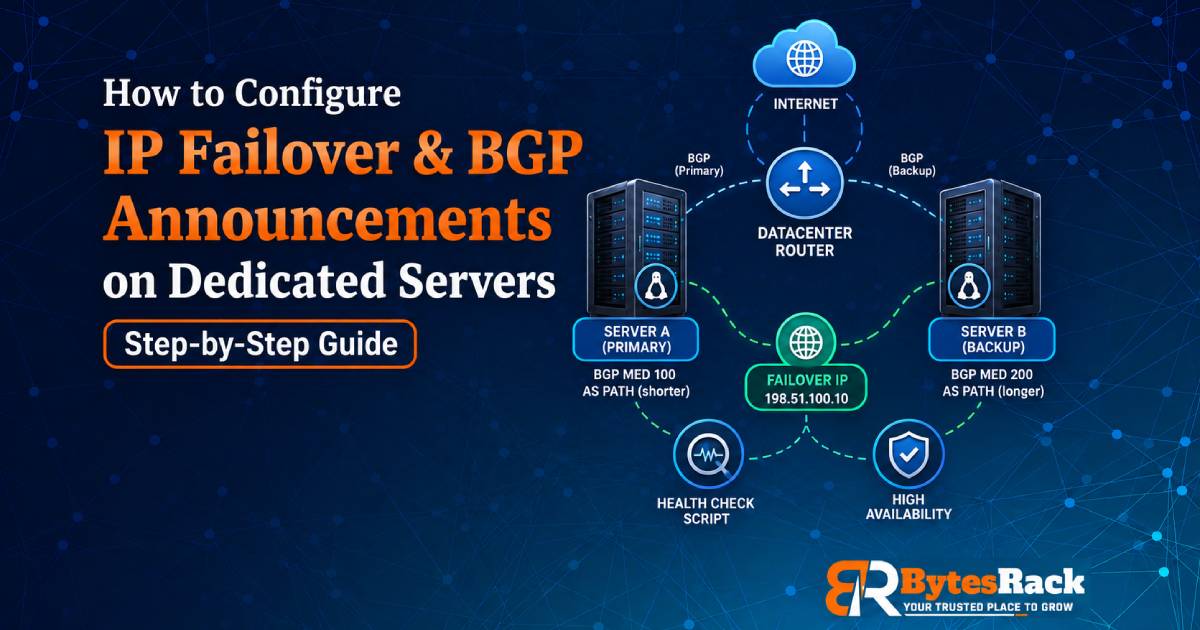
Here is the conceptual breakdown of how to build this architecture using BIRD 2 on Linux (Ubuntu/Debian).
(Note: Insert your Architecture Diagram image here!)
The Prerequisites
Before configuring anything, you need a few things from your datacenter:
- Two dedicated Linux servers (Server A is primary, Server B is backup).
- A provider that offers BGP sessions (You need their neighbor IP, your ASN, and an MD5 password).
- A public IPv4 failover prefix (Usually a /24 or larger).
- Port 179/TCP open between your servers and the provider's router.
The Architecture: How It Actually Works
To make this work, each server carries your Failover IP on a local "dummy" interface. We use a dummy interface instead of your physical network card so that the IP stays active even if a physical cable is unplugged.
We then use a routing daemon called BIRD 2 to announce this Failover IP to the datacenter's router.
Both of your servers will announce the exact same IP address, but with different routing rules:
- The Primary Server announces the route with a highly preferred metric (a low MED value).
- The Backup Server announces the same route, but with a less preferred metric (a higher MED value) and an artificially lengthened path.
Because the router always chooses the shortest and most preferred path, 100% of your traffic goes to the Primary Server. If the Primary Server goes offline, its route disappears, and the router instantly switches to the Backup Server.
The 3 Steps to Implementation
Step 1: The Network Configuration
Instead of touching your main network configuration, you create a virtual "dummy" network interface on both servers. You then assign your shared Failover IP to this dummy interface. This separates your management IP from your service IP.
Step 2: Configuring BIRD 2
Next, you install BIRD 2 on both servers. In the BIRD configuration file, you set up a filter that exports your Failover IP to the datacenter router.
- On Server A, you set the preference metric (MED) to
100. - On Server B, you set the preference metric to
200, making it the passive standby.
Step 3: Automating Health Checks
BGP is smart, but it doesn't know if your actual web application (like Nginx or Apache) has crashed. If Nginx dies but the server is still running, BGP will keep sending traffic to the broken server.
To fix this, you create a simple background Bash script that runs every 5 seconds. The script pings your local web server. If it fails three times in a row, the script tells BIRD to stop announcing the route. The datacenter router instantly notices the route is gone and shifts all traffic to Server B.
Get the Configuration Files
Because long configuration scripts are hard to read on Steemit, I have uploaded the complete network configs, BIRD 2 configuration files, and the Bash health-check script to a secure repository.
Get the Configuration Files
Because long configuration scripts are hard to read on Steemit, I have uploaded the complete network configs, BIRD 2 configuration files, and the Bash health-check script to my blog.
👉 Click here to view and download the full code configurations for this setup
Let me know in the comments if you have ever set up BGP failovers, or if you prefer a different HA method!